 Zero-Trust and Provable Data Privacy
The CISO Zero-Trust AI Checklist From Runtime Isolation to Vendor Access Attestation
Five connected controls stop compromised AI agents before they cause harm.
Anouk Mercer·
 Zero-Trust and Provable Data Privacy
Why Contractual Data Clauses Fail Where Private Inference Infrastructure Succeeds
Technical controls prevent data exposure where contracts can only promise to prohibit it.
Anouk Mercer·
 Zero-Trust and Provable Data Privacy
Bring Your Own Key Is Not Enough for True LLM Output Confidentiality
Encryption alone can't prevent vendors from reading your prompts during inference.
Anouk Mercer·
 Features
How Differential Privacy Actually Works in Deep Learning
Noise added during training protects individual privacy without exposing sensitive data.
Anouk Mercer·
 Features
Why Retrofitting Privacy Into an AI Architecture Rarely Holds
Privacy built into AI systems from the start, not patched on later.
Anouk Mercer·
 Features
Enforcing Data Use Boundaries Between AI Features at Runtime
Runtime enforcement separates AI policy control from the model itself.
Anouk Mercer·
 Zero-Trust and Provable Data Privacy
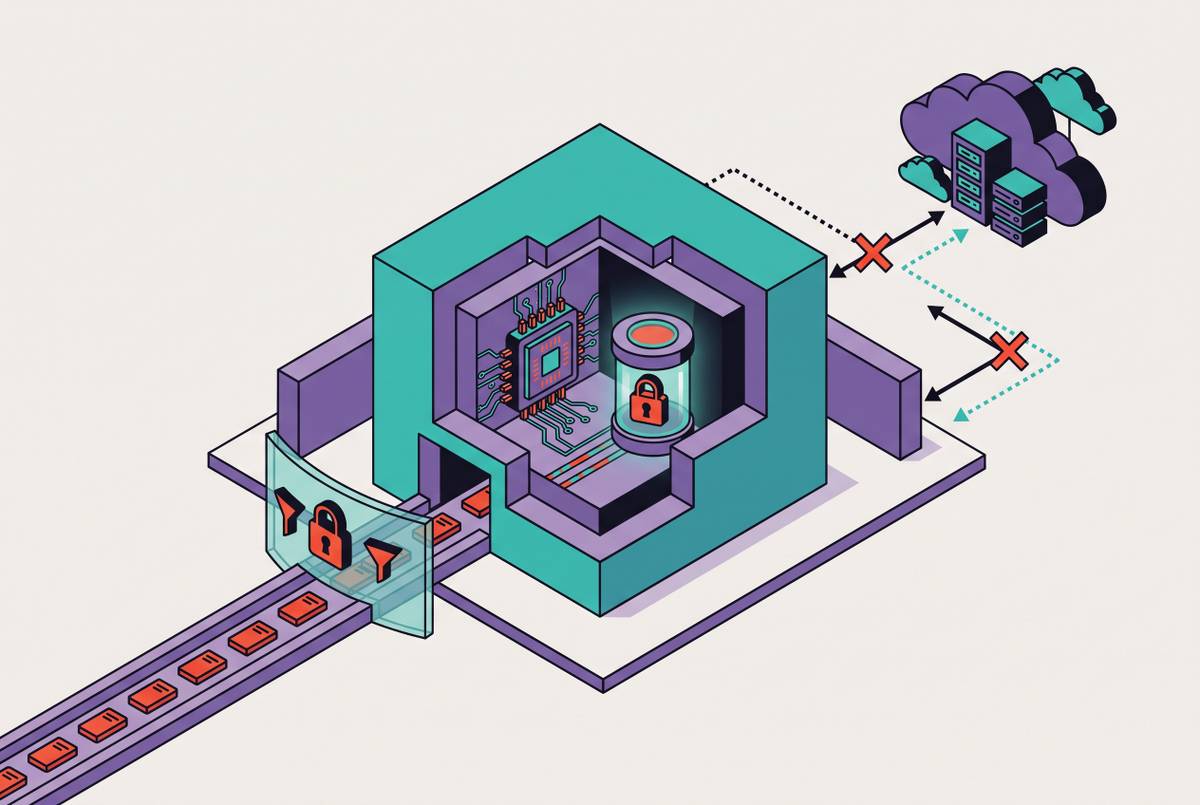
Confidential Computing Enclaves as the Technical Backstop Against AI Vendor Prompt Exposure
Hardware-enforced enclaves prevent cloud providers from reading AI prompts during inference.
Anouk Mercer·
 Private AI Use Cases and Configuration
Attorney-Client Privilege and AI: Which Deployment Models Actually Satisfy Bar Ethics Rules
Consumer AI tools' standard terms make client data retention indefensible under ethics rules.
Anouk Mercer·
 Features
When Synthetic Data Actually Protects Privacy in AI Training
Synthetic data's privacy value depends entirely on generation method, not marketing claims.
Anouk Mercer·
 Zero-Trust and Provable Data Privacy
Verifiable Deletion of Personal Data From Vector Databases
Soft deletion in vector databases leaves personal data physically intact and recoverable.
Anouk Mercer·
 Zero-Trust and Provable Data Privacy
Preventing Model Inversion and Membership Inference in Deployed APIs
API output design is a security decision, not a feature choice.
Anouk Mercer·
 Zero-Trust and Provable Data Privacy
Cryptographic Proof of Data Deletion for AI Training Pipelines
Cryptographic proof replaces procedural assurance for deleting personal data from trained models.
Anouk Mercer·
 Confidential Computing on GPUs
Confidential Federated Learning With GPU TEEs
Hardware-enforced privacy protects federated learning where cryptography alone falls short.
Anouk Mercer·
 Attestation and Verifiable Computing
Confidential Computing Attestation vs TLS Certificate Trust Models
Attestation proves what code is running; TLS only proves you reached the right domain.
Anouk Mercer·
 Private AI Use Cases and Configuration
Configuring Local LLM Inference with Ollama for Data-Sensitive Workflows
Configure Ollama's network and model settings to keep sensitive data fully local.
Anouk Mercer·
 Private AI Use Cases and Configuration
Preventing Sensitive Data Leakage in Enterprise AI Copilot Configurations
Configuration gaps and overpermissioned access drive most data leaks through enterprise AI copilots.
Anouk Mercer·
 Cryptographic Primitives for Private AI
Homomorphic Encryption Schemes for ML Inference Comparison
Choosing the right FHE scheme determines whether ML inference stays private or stays feasible.
Anouk Mercer·
 Trusted Execution Environments (TEEs) and Secure Enclaves
AWS Nitro Enclaves for Sensitive Data Processing
AWS isolates sensitive data processing below the operating system.
Anouk Mercer·
 Trusted Execution Environments (TEEs) and Secure Enclaves
Intel SGX Enclave Development with the Open Enclave SDK
Hardware isolation alone won't protect your secrets without careful boundary design.
Anouk Mercer·
 Trusted Execution Environments (TEEs) and Secure Enclaves
TEE TCB Updates and Patch Management in Production
Patching confidential computing requires tearing down running enclaves to update attestation claims.
Anouk Mercer·
 Trusted Execution Environments (TEEs) and Secure Enclaves
Sealing and Secret Provisioning to SGX and TDX Workloads
Hardware-rooted sealing encrypts enclave secrets for storage, but binds them to a single processor.
Anouk Mercer·
 Trusted Execution Environments (TEEs) and Secure Enclaves
Intel TDX vs AMD SEV-SNP Architecture Differences
Intel centralizes security in firmware, while AMD distributes it throughout the hardware.
Anouk Mercer·
 Zero-Trust and Provable Data Privacy
Zero-Trust Architecture for AI Inference Infrastructure
Zero-trust moves security from perimeters to every workload request in AI inference.
Anouk Mercer·