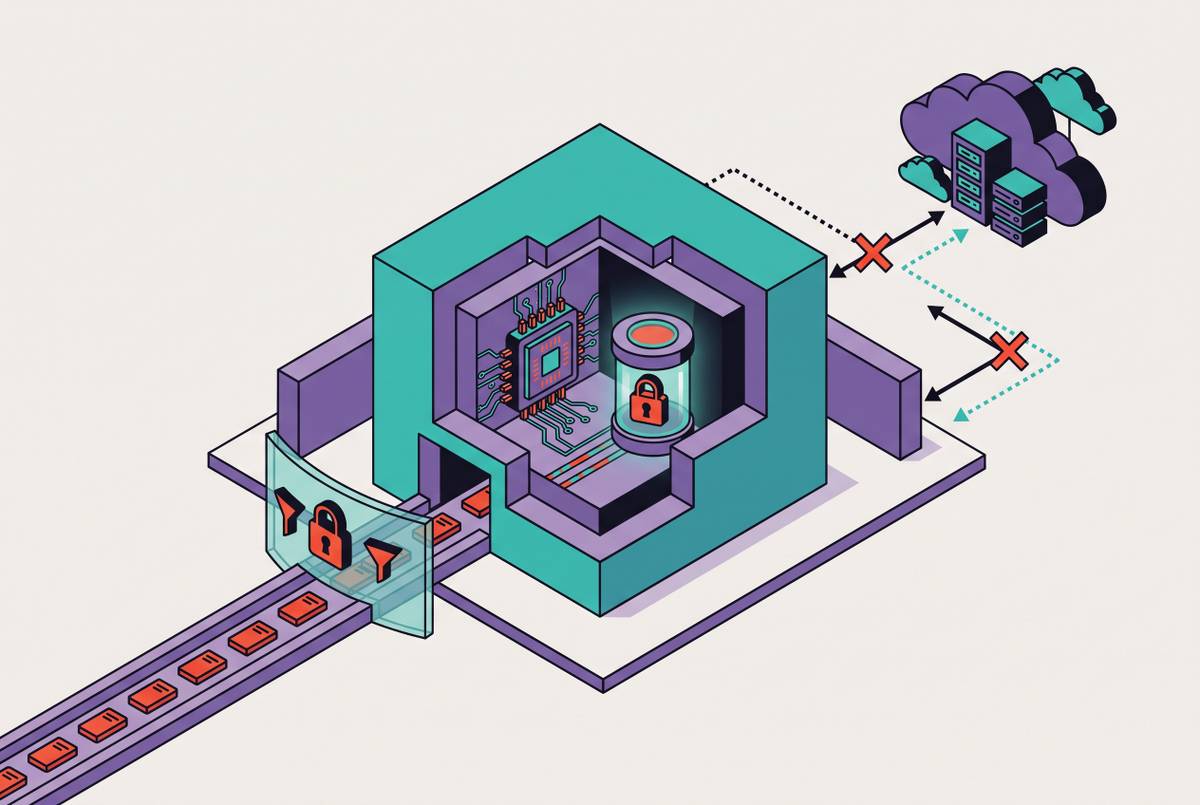
Vendor-Blind AI Deployment Patterns That Make Prompt Exposure Architecturally Impossible
Self-hosted inference and encrypted enclaves make prompt exposure structurally impossible.
Lorena Sundqvist
Section
13 stories in Zero-Trust and Provable Data Privacy.
Self-hosted inference and encrypted enclaves make prompt exposure structurally impossible.
Five connected controls stop compromised AI agents before they cause harm.
Five controls enterprises need to enforce data sovereignty in AI deployments before signing.
Technical controls prevent data exposure where contracts can only promise to prohibit it.
Five operating principles for securing AI agents across enterprise systems.
Encryption alone can't prevent vendors from reading your prompts during inference.
Hardware-enforced enclaves prevent cloud providers from reading AI prompts during inference.
SLSA frameworks built for code need real adaptation to secure AI's multi-stage supply chains.
Soft deletion in vector databases leaves personal data physically intact and recoverable.
API output design is a security decision, not a feature choice.
Cryptographic proof replaces procedural assurance for deleting personal data from trained models.
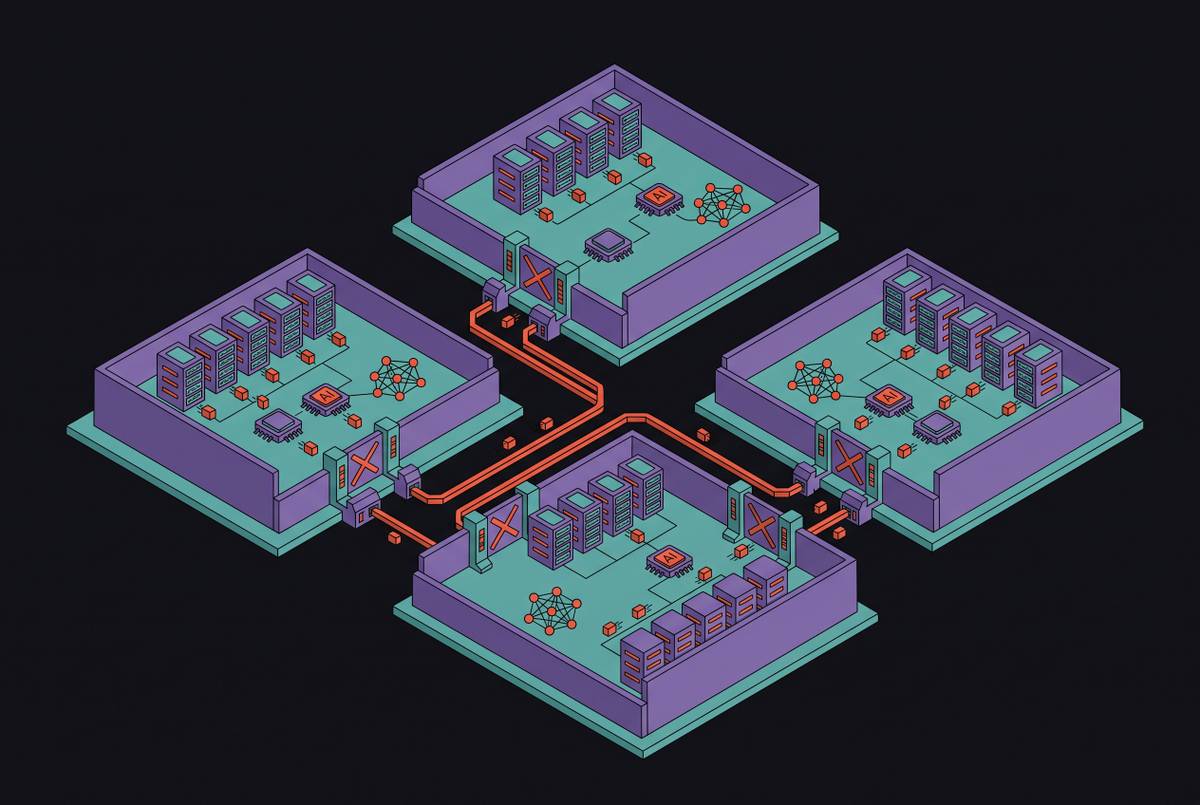
Data residency requires controlling six deployment surfaces, not just where the model runs.
Zero-trust moves security from perimeters to every workload request in AI inference.