Confidential AI Inference at Scale
Multi-Party Inference with Confidential Computing
TEEs offer the only production-speed path to private multi-party inference.
Kian Vance
Senior Writer · · 14 min read
TEEs offer the only production-speed path to private multi-party inference.
Hardware enclaves protect model weights where policy and access controls cannot.
TEEs encrypt prompts inside enclaves, closing the gap TLS leaves behind.
Attestation proves what code is running; TLS only proves who you're talking to.
RFC 9334 defines how remote systems prove their actual runtime state, not just their identity.
Cryptographic logs make it impossible to hide who trained a model or when it changed.
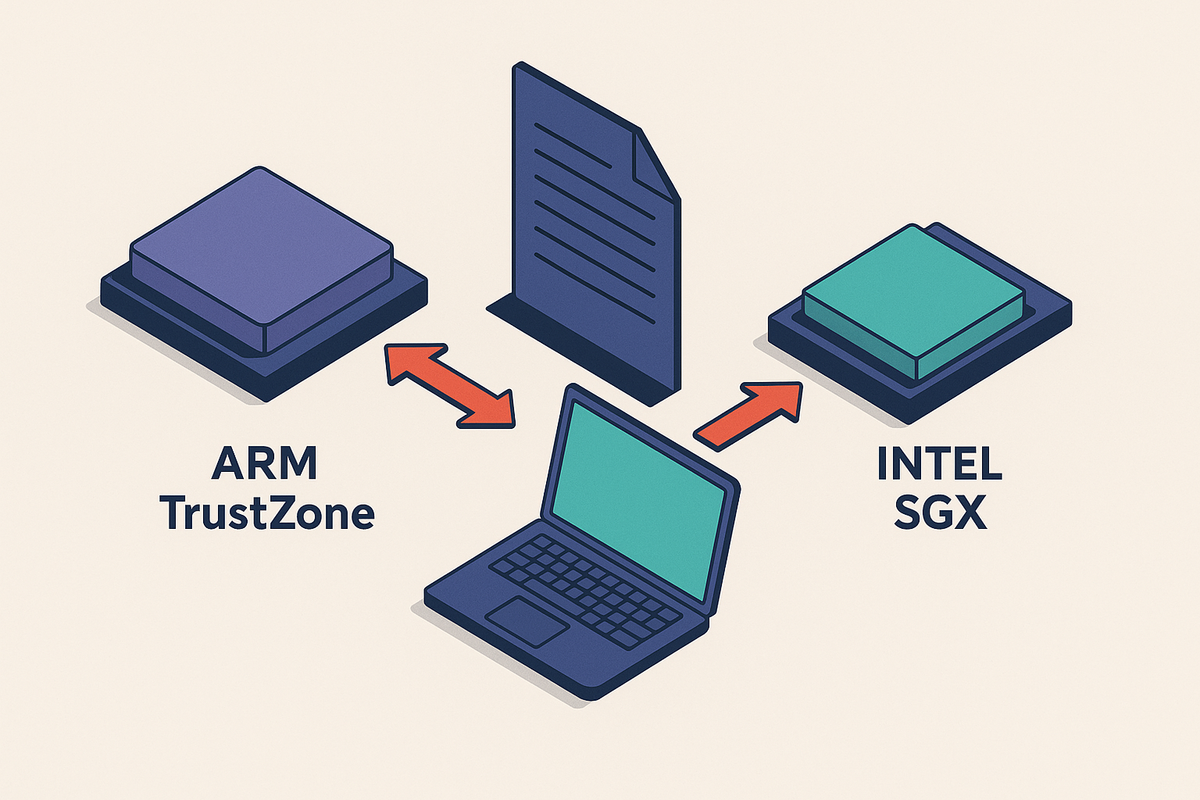
SGX bakes attestation into silicon while TrustZone leaves it to implementers to build.
Attackers replay valid tokens to bypass security checks that depend on current device state.
Measured Boot creates a tamper-proof record of everything that runs before your OS loads.
Cryptographically binding AI models to their provenance without reinventing supply chain security.
Apple's unified memory architecture eliminates the bottleneck that kept AI models off phones.
Learn the configuration settings that keep sensitive data on your own machine.