Features
Enforcing Data Use Boundaries Between AI Features at Runtime
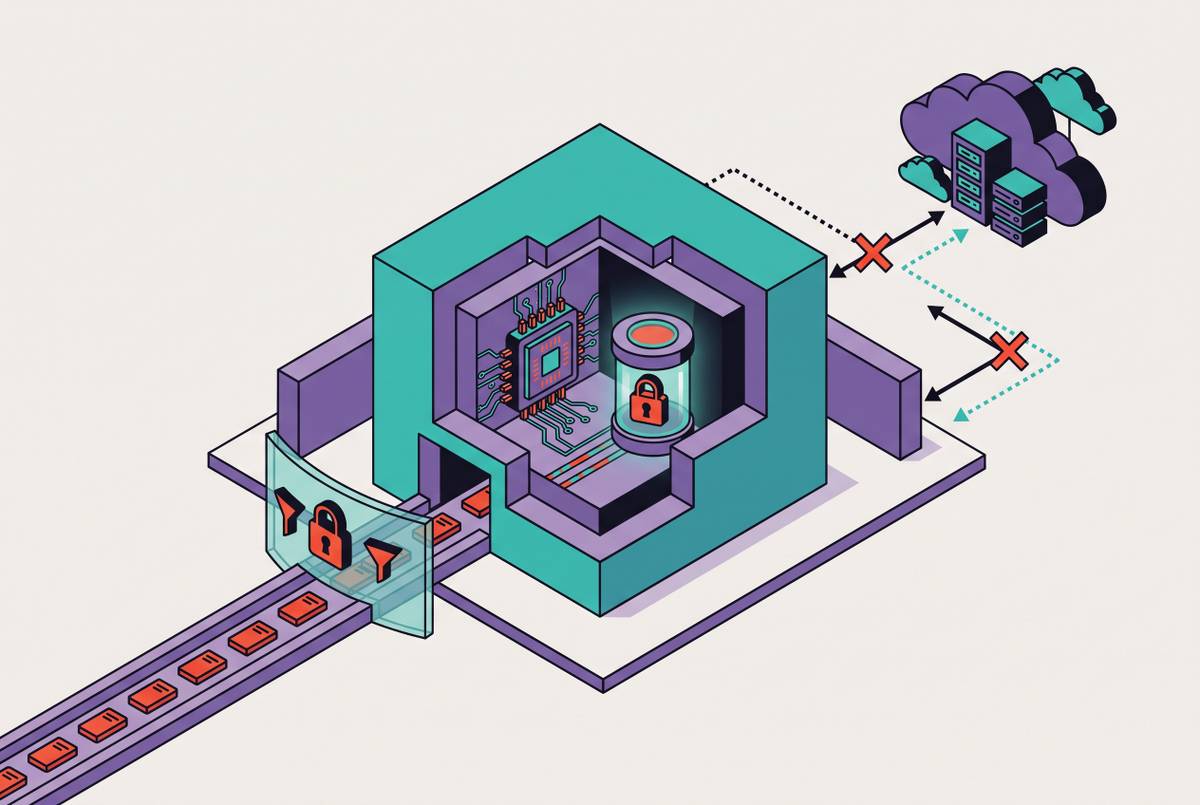
Runtime enforcement separates AI policy control from the model itself.
Anouk Mercer
· 10 min read
Runtime enforcement separates AI policy control from the model itself.
Hardware-enforced enclaves prevent cloud providers from reading AI prompts during inference.
You can add and multiply encrypted data, but only to a fixed depth before noise makes it unreadable.
Governance must track data through the entire AI pipeline, not just to the warehouse.
Consumer AI tools' standard terms make client data retention indefensible under ethics rules.
Privacy policies promise protection that payment doesn't actually deliver or guarantee.
Users can cryptographically verify their AI prompts stay encrypted during processing.
Regulation forced healthcare and finance to adopt federated learning.
Federated learning gains a drift-correction mechanism for non-uniform client data.
Synthetic data's privacy value depends entirely on generation method, not marketing claims.
SLSA frameworks built for code need real adaptation to secure AI's multi-stage supply chains.
Soft deletion in vector databases leaves personal data physically intact and recoverable.