 Private AI Use Cases and Configuration
Off-the-Record AI Conversations Require More Than Incognito Mode
Private mode settings alone won't stop AI providers from retaining your conversations.
Lorena Sundqvist·
 Zero-Trust and Provable Data Privacy
Vendor-Blind AI Deployment Patterns That Make Prompt Exposure Architecturally Impossible
Self-hosted inference and encrypted enclaves make prompt exposure structurally impossible.
Lorena Sundqvist·
 Confidential AI Inference at Scale
Cryptographic Operator Exclusion as a First-Class Design Requirement for AI Assistants
Cryptographic controls, not policy, must exclude operators from AI inference data.
Lorena Sundqvist·
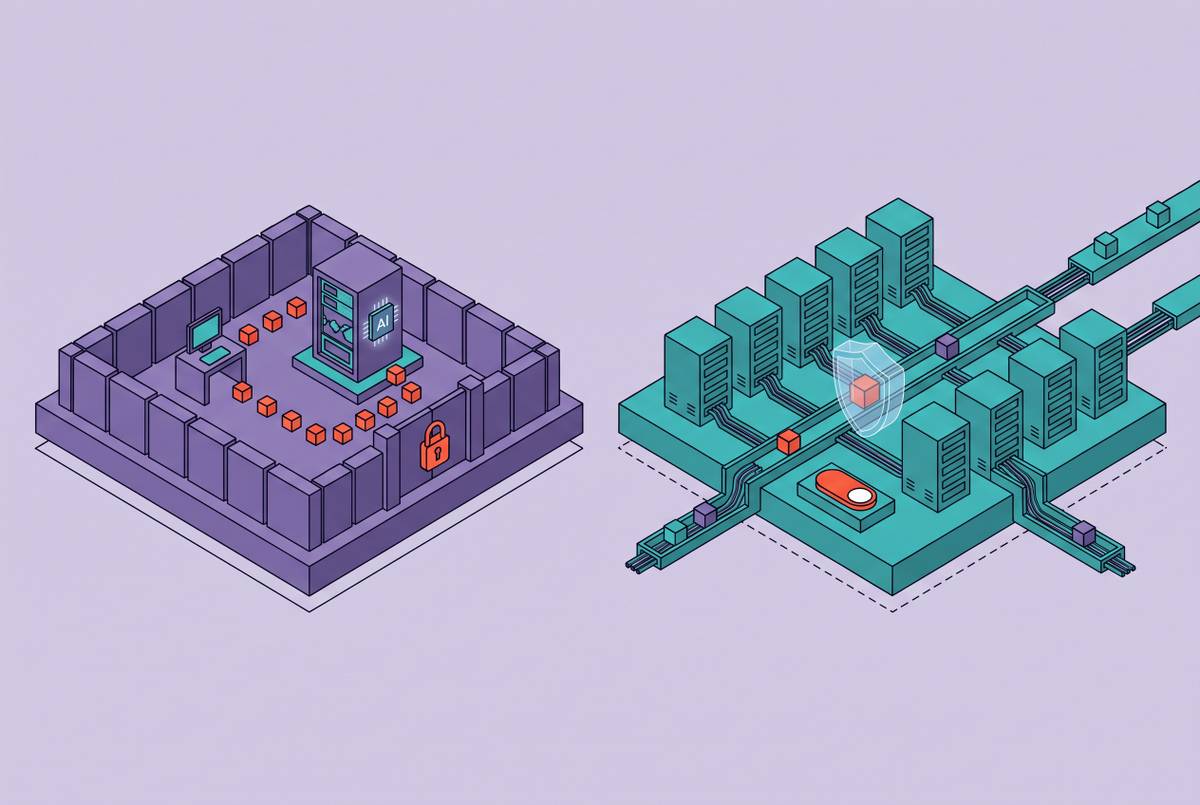 Private AI Use Cases and Configuration
Private Deployment Versus Privacy Mode How to Tell the Difference
Privacy mode restricts how vendors use your data.
Lorena Sundqvist·
 Private AI Use Cases and Configuration
A Practical Workflow Audit for Professionals Introducing AI Into Client Engagements
Professionals must map which data enters AI tools and who reviews outputs before client delivery.
Lorena Sundqvist·
 Confidential AI Inference at Scale
Mapping the TEE Landscape for AI Inference Workloads
Hardware boundaries must protect every step of AI inference, from prompts to outputs.
Lorena Sundqvist·
 Features
What Re-Identification Risk Actually Looks Like in Aggregated AI Telemetry
Quasi-identifiers in AI telemetry can uniquely fingerprint individuals.
Lorena Sundqvist·
 Features
How SCAFFOLD Reduces Client Drift in Federated Learning
Federated learning gains a drift-correction mechanism for non-uniform client data.
Lorena Sundqvist·
 Features
How to Enforce Purpose Limitation in a GDPR-Compliant AI Pipeline
Build purpose boundaries into your AI pipeline from data collection onward.
Lorena Sundqvist·
 Zero-Trust and Provable Data Privacy
Data Residency Enforcement in Multi-Region AI Deployments
Data residency requires controlling six deployment surfaces, not just where the model runs.
Lorena Sundqvist·
 Confidential Computing on GPUs
CPU-GPU Confidential Channel Establishment with AMD SEV-SNP
Researchers show how to encrypt GPU memory channels in confidential AMD VMs.
Lorena Sundqvist·
 Confidential AI Inference at Scale
Latency and Throughput Overhead of TEE-Protected Inference
TEE overhead concentrates at memory boundaries, not compute.
Lorena Sundqvist·
 Confidential AI Inference at Scale
Model Weight Protection Inside Confidential Inference Servers
Plaintext model weights in memory can only be protected by hardware, not policy.
Lorena Sundqvist·
 Attestation and Verifiable Computing
Verifiable Transparency Logs for Model Provenance
Cryptographic logs can prove a model's training history wasn't altered after release.
Lorena Sundqvist·
 Attestation and Verifiable Computing
Attestation Token Replay and Freshness Attacks
Valid tokens become dangerous weapons when presented outside their intended time window.
Lorena Sundqvist·
 Cryptographic Primitives for Private AI
Post-Quantum Cryptography Migration for AI Inference APIs
Quantum computers threaten AI traffic captured today and decrypted later.
Lorena Sundqvist·
 Trusted Execution Environments (TEEs) and Secure Enclaves
Confidential Containers with Kata Containers and TEE Backends
Kata Containers protects workloads from the infrastructure itself using hardware-encrypted memory.
Lorena Sundqvist·
 Trusted Execution Environments (TEEs) and Secure Enclaves
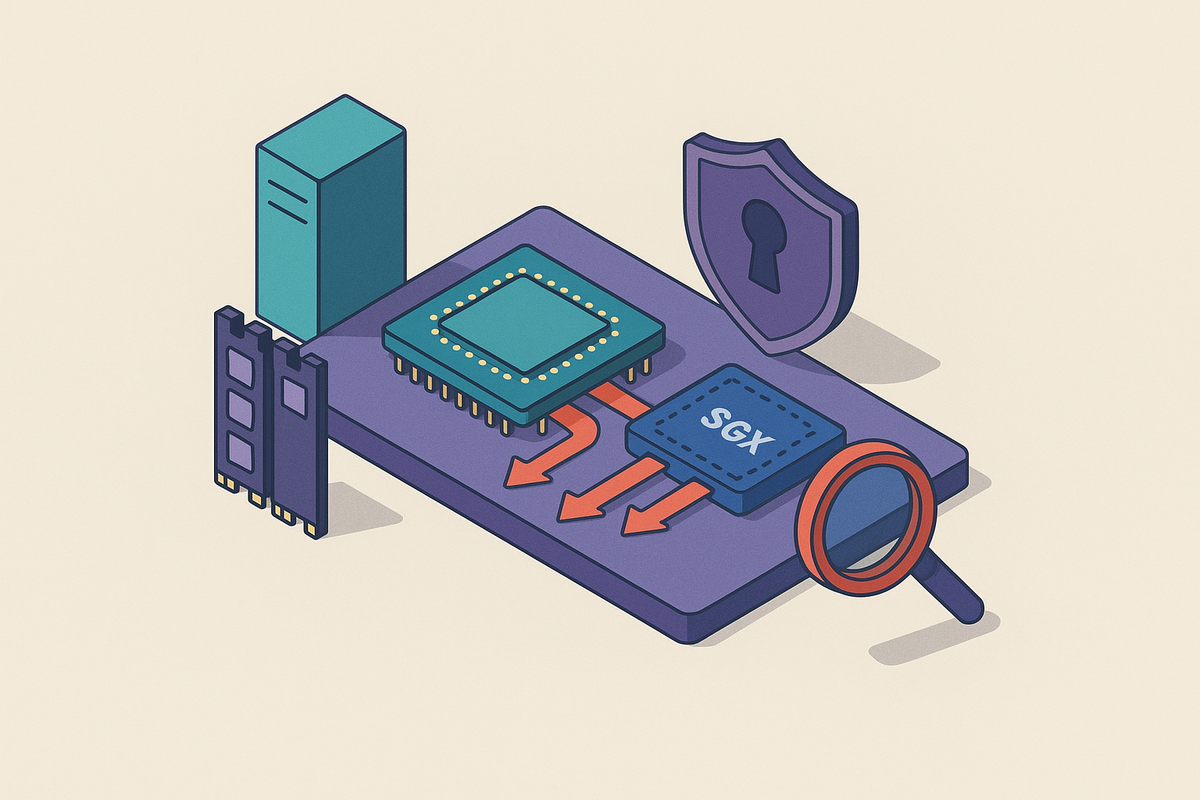
Side-Channel Attack Surfaces in SGX Enclaves
OS-level adversaries can extract secrets from SGX enclaves through deterministic side channels.
Lorena Sundqvist·
 Confidential Computing on GPUs
NVIDIA H100 Confidential Computing Mode Architecture
NVIDIA's H100 encrypts GPU memory to shield AI model weights and data during computation.
Lorena Sundqvist·